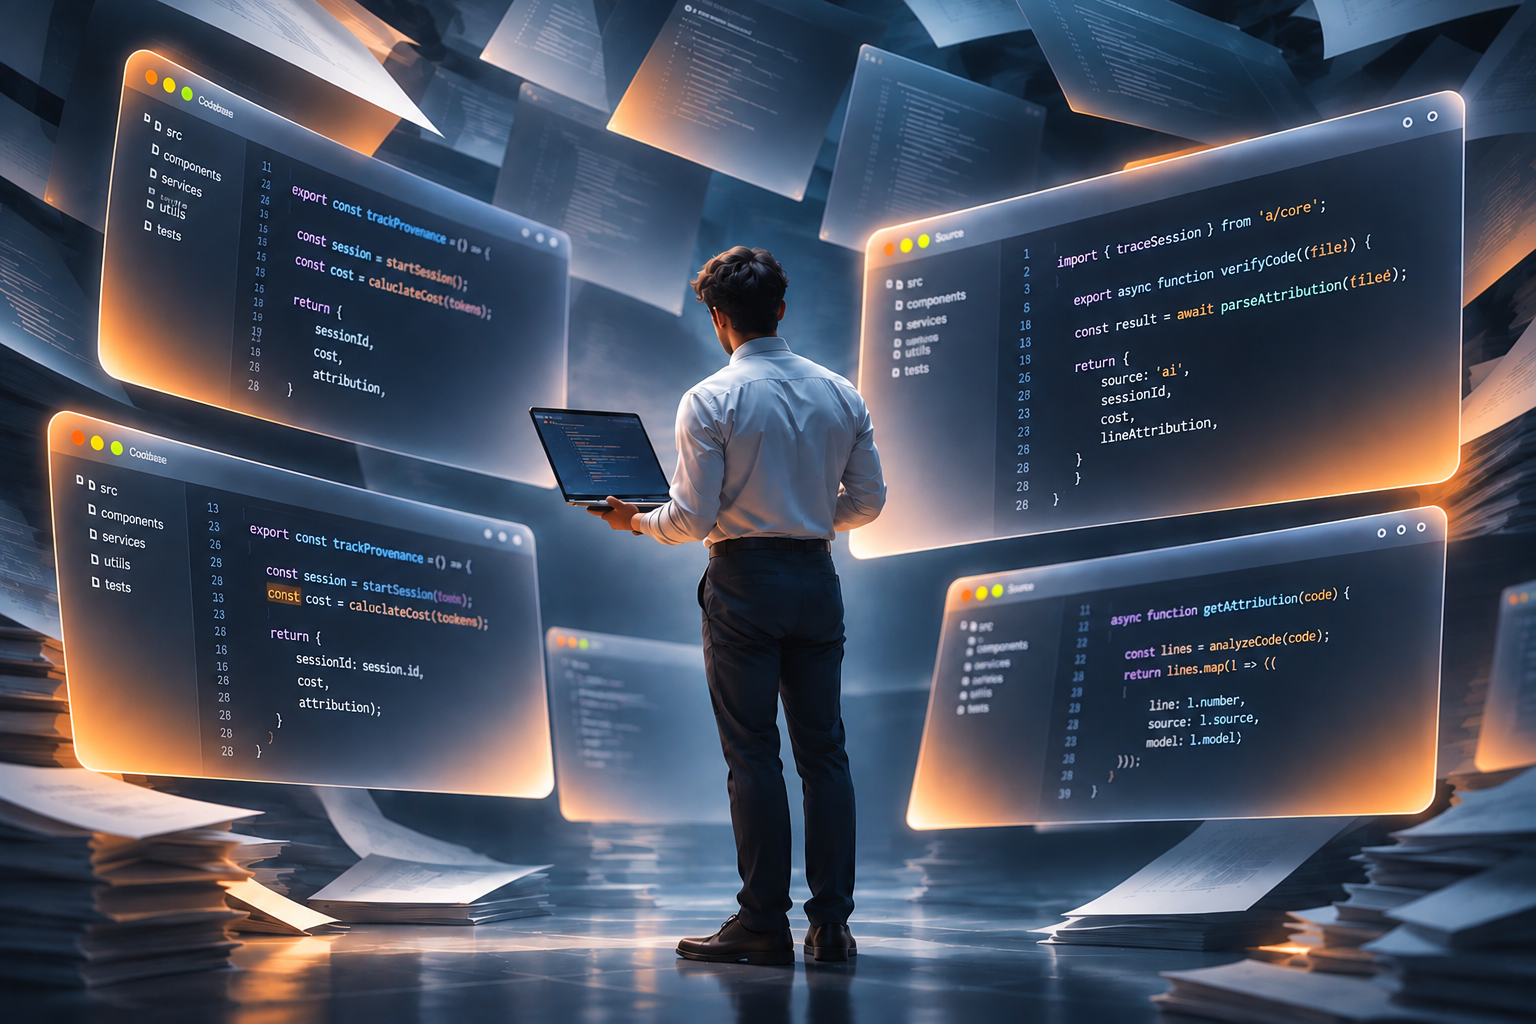
Built from scratch as a production-ready AI code provenance platform, Origin tracks AI-generated code, prompts, sessions, costs, and line-level attribution across multiple coding agents. Its Git-native architecture preserves coding history and context while supporting team-wide governance, secure workflows, and scalable operation across 100K+ tracked commits.


Origin needed to capture activity from 8 different AI coding agents, each exposing prompts, sessions, models, token usage, and code changes through different hooks, transcript files, or local databases. All of that data had to be normalized into one consistent provenance format without disrupting developers’ existing workflows.
Line-level AI attribution had to remain accurate even after developers rebased, squashed, amended, or cherry-picked commits. Because those operations can change commit hashes and repository history, Origin needed a reliable way to preserve provenance across real-world Git workflows.
Origin stores prompts, session metadata, and code provenance inside Git-based workflows. This created a security challenge: sensitive information and secrets had to remain protected across repositories, clones, and forks while keeping provenance portable and useful for governance.
Let our team find the best tech approach for your business scale and scope.






Every pull request runs GitHub Actions with ESLint, type checking, around 6,400 Vitest tests, dependency audits, secret scanning, and Docker builds. Staging deploys automatically to Fly.io, while production releases use manual approval, rolling deployment, health checks, and traceable versioning tied to Git SHA.
Origin was built around a local TypeScript/Node.js CLI with hooks for 8 AI coding agents, Git-native storage, a local SQLite index, an MCP server, and an optional hosted dashboard. This architecture captures prompts, diffs, models, tokens, costs, snapshots, and line-level attribution without forcing developers to change their existing workflows.
Better Stack centralizes logs, Sentry tracks application errors, and Fly.io Prometheus metrics feed Grafana dashboards for latency, error rate, CPU, and memory. Uptime checks, Slack alerts, budget alerts, health commands, and rolling deployments help the team detect and recover from issues quickly.
Origin applies 19 automatic redaction rules before data leaves the developer’s machine and scans commits against 41 secret patterns. Metadata-only Git notes, AES-256-GCM encrypted prompts, scoped API keys, workspace roles, audit logs, rate limiting, and hardened web headers protect sensitive code and prompt data.
Every AI-written line links back to the agent, model, and prompt that produced it, even after rebase and squash.
Every agent turn is snapshotted, so changes can be rewound or restored in one command.
63 releases shipped with rolling deployments and no customer downtime.
19 redaction rules remove secrets before any data leaves the developer’s machine.


Subscribe to our newsletter and get the latest insights that help you stay ahead of the curve.

© 2017-2025 All rights are reserved